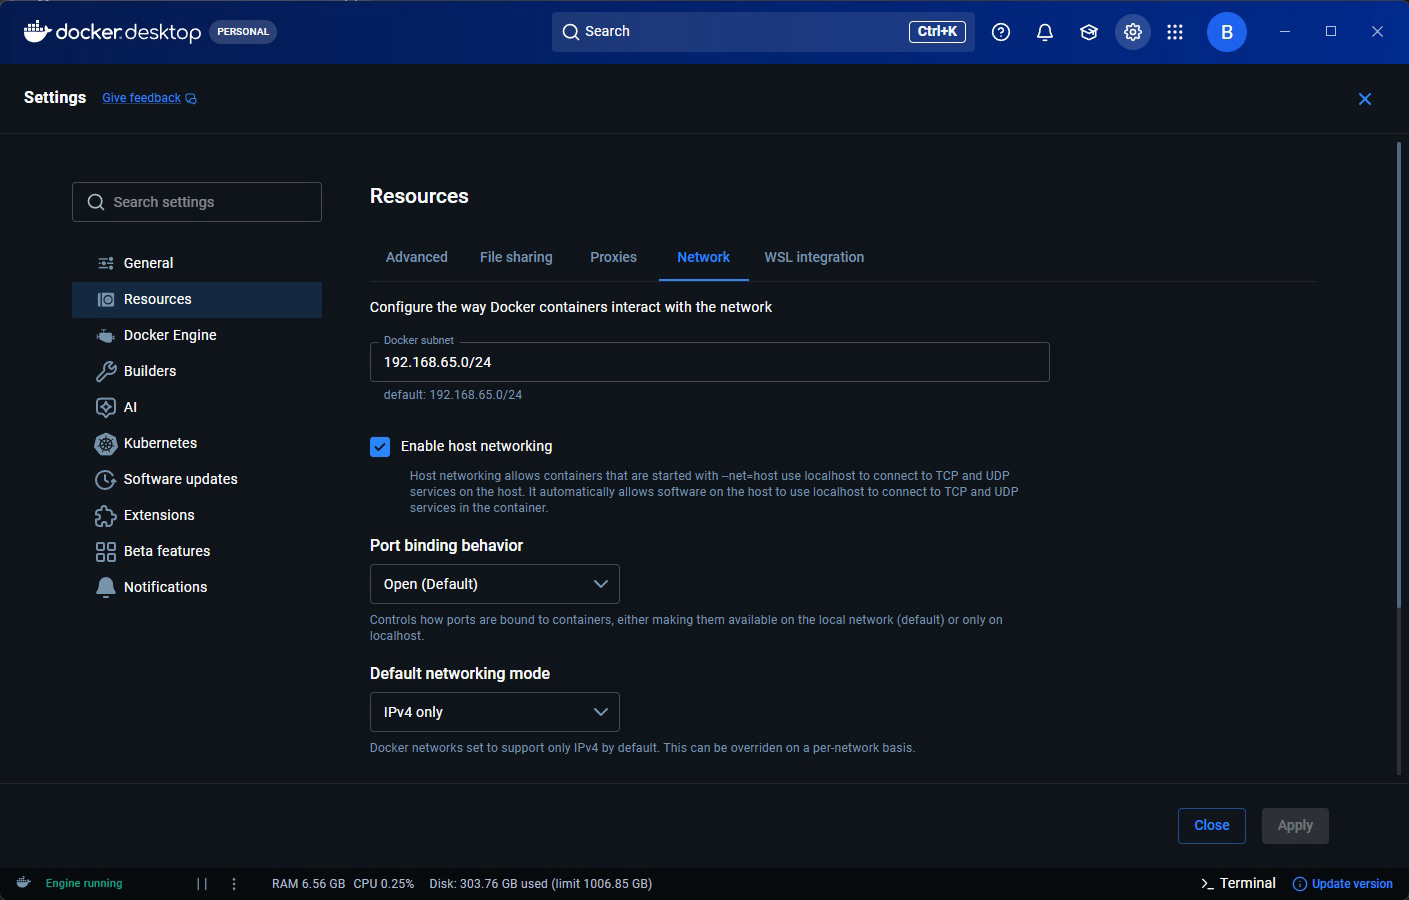
@lemmyvore@feddit.nl , I already made the JSON file changes, but seeing as this hasn’t changed in Jellyfin reporting after doing so, I think we can point to this as being authoritative for how it appears in Jellyfin logs. But I do have it listed as a known proxy, and I added that X-Forwarded-For header to NPM, so I’m not sure what else I’m missing. With a /24 subnet, this IP address is probably safe though, right?
Thanks!
@lemmyvore@feddit.nl , I already made the JSON file changes, but seeing as this hasn’t changed in Jellyfin reporting after doing so, I think we can point to this as being authoritative for how it appears in Jellyfin logs. But I do have it listed as a known proxy, and I added that X-Forwarded-For header to NPM, so I’m not sure what else I’m missing. With a /24 subnet, this IP address is probably safe though, right?